
CoreBiz IT Services & CRM
Choose workspace roles with purpose
List who needs to read records, who edits them and who manages membership.
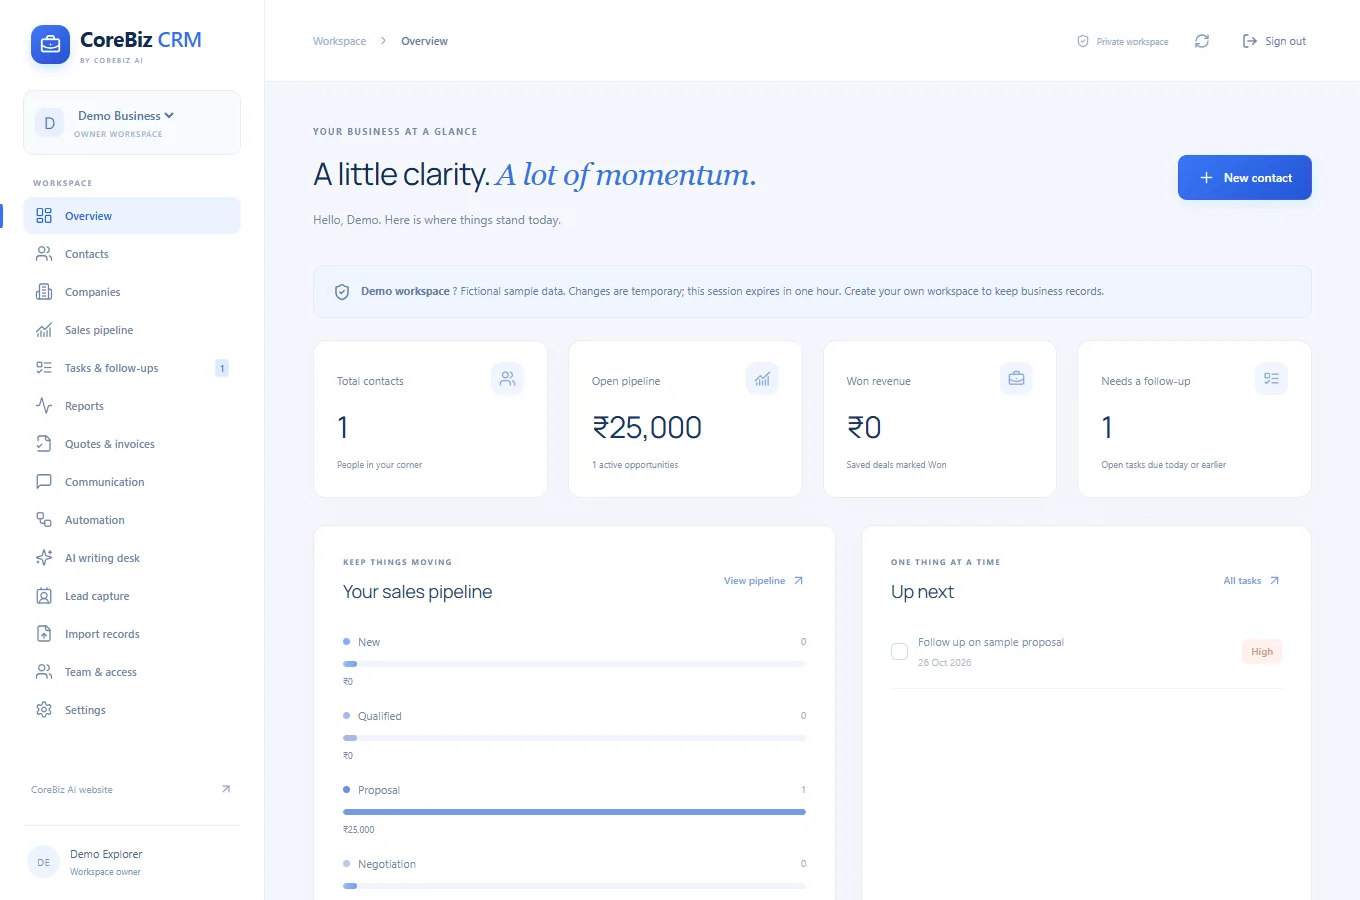
This guide uses CoreBiz IT Services & CRM as its starting point. It combines the documented project capabilities with practical suggestions for planning and reviewing your own work. The suggestions below are guidance, not a claim that the application automates every step.
Start with a concrete task
List who needs to read records, who edits them and who manages membership. Give each teammate a role that matches those responsibilities.
Start with responsibilities rather than job titles
A workspace role should reflect what a person needs to do inside that workspace. A senior colleague may only need to review information, while a coordinator may need to update records throughout the day. Job titles alone do not describe the access required for either task.
Write down the actual responsibilities before assigning a role. Identify who maintains records, who reviews progress and who manages membership. This makes it easier to explain an access decision and to change it when a person's work changes.
The CoreBiz CRM distinguishes administrators, editors and viewers. Use those documented roles rather than assuming the application supports an arbitrary custom permission for every possible action. If a requirement falls outside the available model, discuss the limitation before putting sensitive work into the workspace.
Keep ownership and shared access understandable
A person can work in their own workspace and in a shared workspace. That flexibility is useful, but it creates a responsibility to know which context is active before creating or changing a record. Similar-looking screens can contain different teams' information.
Include the workspace identity in the team's handover instructions. A request to update the customer record is incomplete if the same colleague participates in several workspaces. Name the relevant workspace and record so the instruction does not depend on guesswork.
Do not use a personal workspace as an informal substitute for a shared business process without considering continuity. If other people need to maintain the records, agree how ownership and access will work before the information becomes essential to daily operations.
Use a fictional team to test the role choices
Imagine a three-person service business. One person manages membership, another maintains contacts and opportunities, and a third reviews progress before a weekly meeting. Those responsibilities suggest different access needs even though everyone participates in sales discussions.
The reviewer may not need editing access simply because they attend the meeting. The record keeper may need to edit business information without being responsible for inviting new members. The administrator should understand that membership management affects who can see and change the workspace.
Test the arrangement with a harmless sample record and the intended roles. This example describes a review method, not a claim that every possible permission combination exists. Confirm the behavior of the actual role model before relying on an assumed restriction.
Make onboarding include context as well as access
An invitation gives a person entry to a workspace, but it does not explain how the team uses it. Provide a short introduction to naming conventions, important records and the process for correcting mistakes. Without that context, a well-intentioned colleague can create inconsistent data immediately.
Explain which actions require a conversation before a change. For example, the team may want a shared review before reorganizing pipeline records or altering important customer details. Such operating rules are separate from technical permissions and should not be presented as automatically enforced by the application.
Give the new member a clear way to ask questions. A person who is unsure which company record to use should not have to choose between guessing and abandoning the task. A small amount of guidance at the start prevents confusing records later.
Review access when responsibilities change
Membership should be reviewed when a colleague changes role, finishes a temporary assignment or leaves the team. Waiting for a general cleanup can leave access in place after the original reason has ended. Include the review in the actual handover process.
Before revoking access, ensure the remaining team understands any unfinished work. Removing membership does not by itself transfer the knowledge behind an open opportunity or an upcoming follow-up. Record the current status and next action through the appropriate shared process.
Check the result after the change using the available administrative view. Do not assume that a conversation about leaving the project has changed application access. The technical membership and the team's understanding should agree.
Handle mistakes without broadening permissions unnecessarily
If a colleague cannot complete a task, first identify what they are trying to do and in which workspace. The problem may be an incorrect context or an unclear process rather than an insufficient role. Giving everyone administrator access can hide the immediate issue while creating wider responsibilities.
When a role change is appropriate, document its purpose and review whether it is temporary. A short assignment can otherwise become a permanent expansion of access. Keep the decision connected to the work rather than to the convenience of avoiding another access request.
A useful workspace policy is simple enough that the team can follow it. It should explain who manages membership, how changes are requested and when access is reviewed. The goal is understandable collaboration with appropriate boundaries, not a complex rulebook that nobody uses.
What the project provides
Invite teammates as administrators, editors or viewers. Switch between your own and shared workspaces. Server-side permissions protect changes and membership can be revoked.
Review the result before moving on
Review access when a role changes or a colleague leaves. Revoking workspace membership should be part of the handover checklist rather than an occasional cleanup.
Access and setup
Use admin / admin to explore an isolated one-hour demo with fictional records. For persistent business data, create your own email/password account. Owners can generate seven-day invitation links for teammates with matching account emails. Email recovery and verification, online payment links and AI writing require dedicated providers to be configured later.
Common questions
Who should review a temporary access change?
The person responsible for workspace membership should understand why the change is needed and when the responsibility ends. Agree on a review point when granting access for a short assignment. If the work changes, revisit the decision rather than allowing a temporary arrangement to become permanent by default. Include the affected workspace in the request, because a person may participate in several different contexts.
A short record of the reason helps later administrators distinguish an intentional role from an accidental leftover. The operating review complements the application's permission enforcement; neither should be mistaken for a complete substitute for the other.
Where can I find the current project details?
Read the CoreBiz IT Services & CRM project page for its documented features, access notes and live application link.
Does this guide describe an automated workflow?
Only the capabilities explicitly described in the project section are product features. Planning and review suggestions may need to be performed manually.
Your next step
To explore a similar experience for your own audience, review our related service. Start the discussion with a concrete user task and the information needed to complete it.